
No Person has a better attack on AES-128 than attempting all of the keys, so its 128 bits is close to a statement about the design itself. A bit count in lattice-based cryptography is a statement about the state of cryptanalysis, and it strikes when the cryptanalysis moves, in both direction. That announcement also closed the standardisation course of that started with the 2016 call. A draft normal for HQC shall be printed for comment and a last version is anticipated roughly two years afterwards, so the second key encapsulation mechanism just isn’t a shipping product but. The fourth round closed in March 2025 with the choice of HQC and nothing else.
2Four Encryption And Decryption Example
All lattice primarily based cryptography is comparatively new, and module based systems are even newer. We are still trying to analyze the methods https://med4net.ru/referat.html, and assaults that shave off a few of the security continue to be discovered. Our initial uses of those cryptographic methods will doubtless be mixed with our classical methods known as hybrid techniques. A Kyber key and an ECC key are used to generate a single session key which uses both the Kyber parts and the ECC parts. If certainly one of these methods is compromised, the key is nonetheless safe.
Three Minimal Distance And Shortest Vector Problems

The key trade normal for the American federal authorities and, through browser deployment, for a majority of web traffic rests on Module-LWE. The compact signature scheme awaiting its normal rests on NTRU lattices. A Number Of of the leading candidates in NIST’s signature on-ramp rest on multivariate or code assumptions particularly to avoid including to that pile. This is why the serious work in deploying lattice-based cryptography isn’t algorithm choice. NIST’s alternative of ML-DSA over Falcon because the general-purpose signature is strictly that desire expressed as a standard.
Working on units of vectors isn’t very convenient, so the lattice foundation is often represented as an array. The vectors themselves kind the columns and every worth within the vector types a row. This lets you use regular matrix operations to do calculations within the lattice.
- Signatures in lattice-based cryptography have a attribute vulnerability to this, and it was described early.
- According to coverage from CryptoSlate and crypto.information, Hoskinson went further, accusing Buterin of “bag-holding too much hash-based crypto research” and arguing that no credible new attack has truly surfaced to justify rushing larger keys or an early migration.
- An algorithm that is sound on paper and carried out in a way that leaks timing is an insecure system.
- Signing is therefore several times slower than the arithmetic alone would counsel, which is the price of a signature that provably tells you nothing.
Two of them have lost a flagship scheme to a classical attack up to now few years, none of them lattice-based cryptography, which is the strongest available argument for keeping more than one. In ML-DSA the key era samples a public matrix from a seed and two short secret vectors, publishing the matrix together with their combination. The response is the masking vector plus the challenge multiplied into the primary secret vector. ML-KEM does not return an error, as a end result of an error message is itself data an attacker can farm across many queries. As A Substitute it performs what FIPS 203 calls implicit rejection, returning a pseudorandom worth derived from the ciphertext and a secret stored within the decapsulation key, so that a malformed question yields a key that’s incorrect however indistinguishable from a proper one.
Bob will keep his private key secret, which he will use to decrypt Alice’s message. Notice that it is infeasible for an eavesdropper to find out the personal key solely from the common public key. By providing standardized post-quantum cryptography (PQC) algorithms, researchers can create cryptographic techniques which would possibly be secure in opposition to each quantum and traditional computers and might interoperate with present communication protocols and networks. If the attacker can get you to make use of a cooked A matrix, then he may give you a matrix that he can discover the personal key s through a special function that knows tips on how to reverse cooked A. Kyber specifies A generated with a prf which ensures A might be random.
Lll And What Polynomial Time Buys
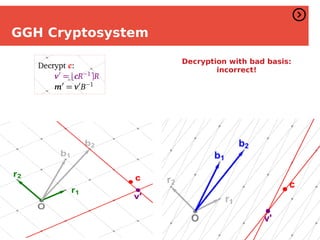
Regev’s discount runs a quantum step, which is certainly one of the stranger details in the topic. Buterin pointed to the overall number area sieve, the algorithm that forced RSA’s key sizes to balloon, as a precedent for what AI-driven math analysis may do to lattice problems inside two years. We explored the implementation of NTRUEncrypt(Nth Degree Truncated Polynomial Ring Unit).It is mainly a lattice based alternative to traditional crypt algorithms like RSA which makes use of Shortest Vector Problems in lattice. Lattice is an infinite association of equidistant points in a vector area.
The summary famous that previously no polynomial and even subexponential time quantum algorithm was recognized for those issues at any polynomial approximation factor, so if correct the paper would have moved a boundary that had not moved in twenty years. The methods were unfamiliar too, utilizing Gaussian functions with advanced variances and a windowed quantum Fourier remodel. Chris Peikert gave a classical reduction in 2009 for a variant of GapSVP at the value of an exponentially large modulus, and Zvika Brakerski, Adeline Langlois, Chris Peikert, Oded Regev and Damien Stehlé produced a broader classical hardness end in 2013. None of this impacts follow, as a end result of deployed parameters are chosen towards concrete attacks somewhat than by following the reductions, however it issues for the way a lot the speculation is actually promising. The structure Shor exploits is not current, the generic quantum speed-up is just quadratic, and thirty years of concentrated effort by individuals who would very very similar to to publish the opposite outcome haven’t produced an assault.
Nonetheless, when using Goppa codes, the Niederreiter cryptosystem reaches equivalent safety to the McEliece cryptosystem, whereas additionally being quicker. It features in an analogous way to McEliece’s proposal but uses a parity-check matrix HH somewhat than a generator matrix GG. Secondly, Eve could attempt to determine the message mm immediately from the ciphertext cc without discovering GG. In different words, Eve is making an attempt to decode a random linear code with tt errors, which is confirmed to be NP-hard 10.
There are two ways to build the oracle inside BKZ, they usually have reverse shapes. Enumeration searches a tree of candidate coordinate vectors, taking time superexponential within the block measurement however only a polynomial quantity of reminiscence. Sieving keeps an exponentially large listing of lattice vectors and repeatedly combines them into shorter ones, taking exponential time and exponential reminiscence. Choosing parameters in lattice-based cryptography subsequently reduces to a single question, which is how giant b must be earlier than BKZ solved your instance. Reply that and multiply by the worth of the oracle, and you have a safety estimate. What LLL guarantees is a vector not than roughly two to the facility of the dimension instances the true shortest, and that certain decays exponentially, so in dimension eight hundred the guarantee is nugatory.